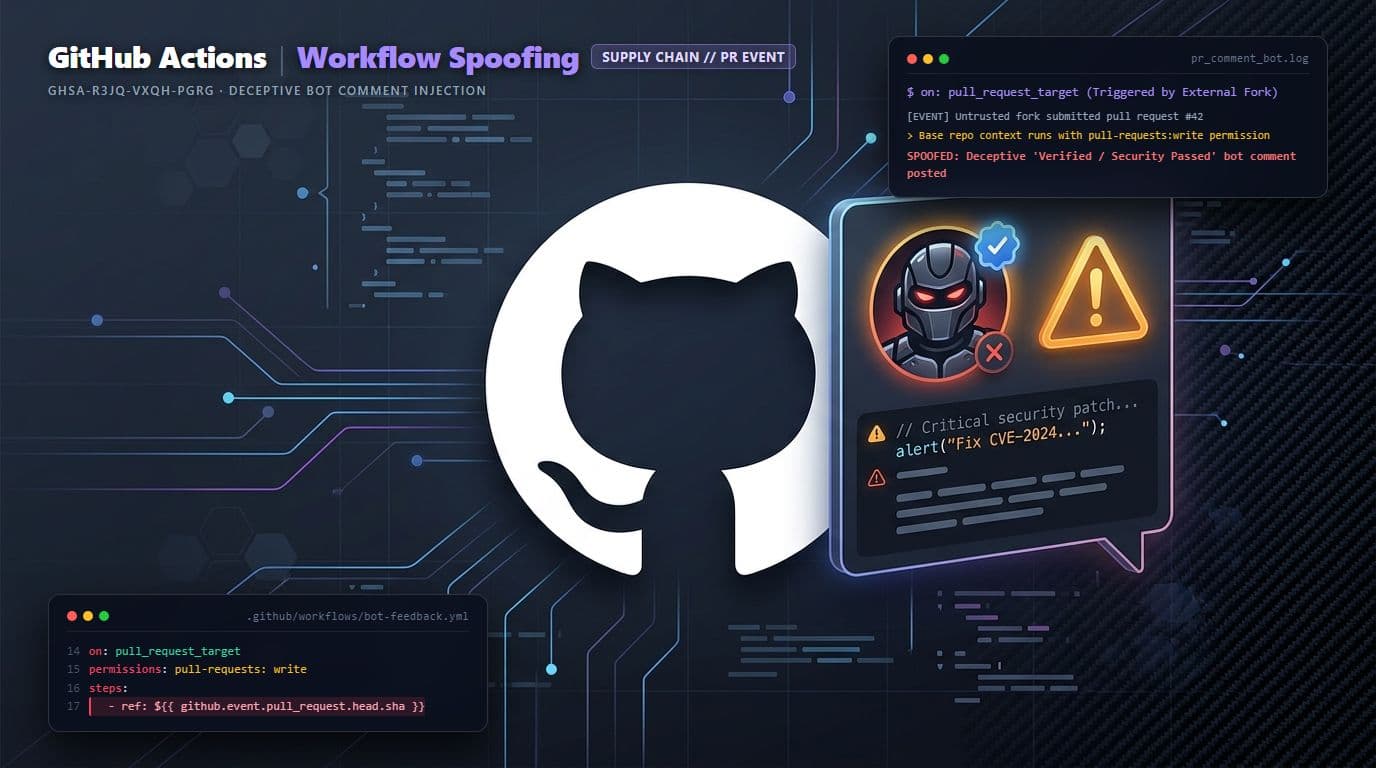
Executive Summary
Modern CI/CD pipelines often execute automated validation, test coverage feedback, and bot comments on pull requests. During an audit of BigBlueButton's automated GitHub Actions workflows, a logic flaw was discovered in how pull request events from untrusted forks were handled, permitting automated bot spoofing or deceptive comment posting.
Coordinated Disclosure Timeline
CI/CD pipeline security review conducted on GitHub Actions workflows.
Flaw identified in pull_request_target / bot comment triggers.
Reported to BigBlueButton maintainers with remediation proposals.
Maintainers secured workflow triggers, permissions, and published GHSA-r3jq-vxqh-pgrg.
01.GitHub Actions Context & The pull_request_target Pitfall
Workflows triggered on 'pull_request_target' run in the context of the base repository rather than the untrusted fork, providing access to repository secrets and write permissions (such as pull-requests: write). If workflow steps blindly interpolate user-controlled inputs or check out untrusted head branches, severe security vulnerabilities arise.
name: PR Automated Feedback
on:
  pull_request_target:
    types: [opened, synchronize]

permissions:
  pull-requests: write

jobs:
  bot-comment:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
        with:
          ref: ${{ github.event.pull_request.head.sha }}
      # Executes untrusted scripts or processes manipulated title/body
- run: npm run analyze-pr02.Deceptive Social Engineering Vector
Because the bot carries official badges or repository collaborator status, forged or manipulated status messages can deceive maintainers or downstream contributors into believing that malicious commits passed automated security verification or were approved by automated gates.
Reproduction & Proof of Concept (PoC)
Demonstration of comment crafting via structured fork submission.
- Fork the target repository into an independent account.
- Construct a pull request containing crafted payload variables in metadata fields.
- Trigger the automated CI pipeline action.
- Observe the privileged workflow executing the bot command and publishing arbitrary comment content with repository bot authorization.